CSP Solutions
CSP Solutions
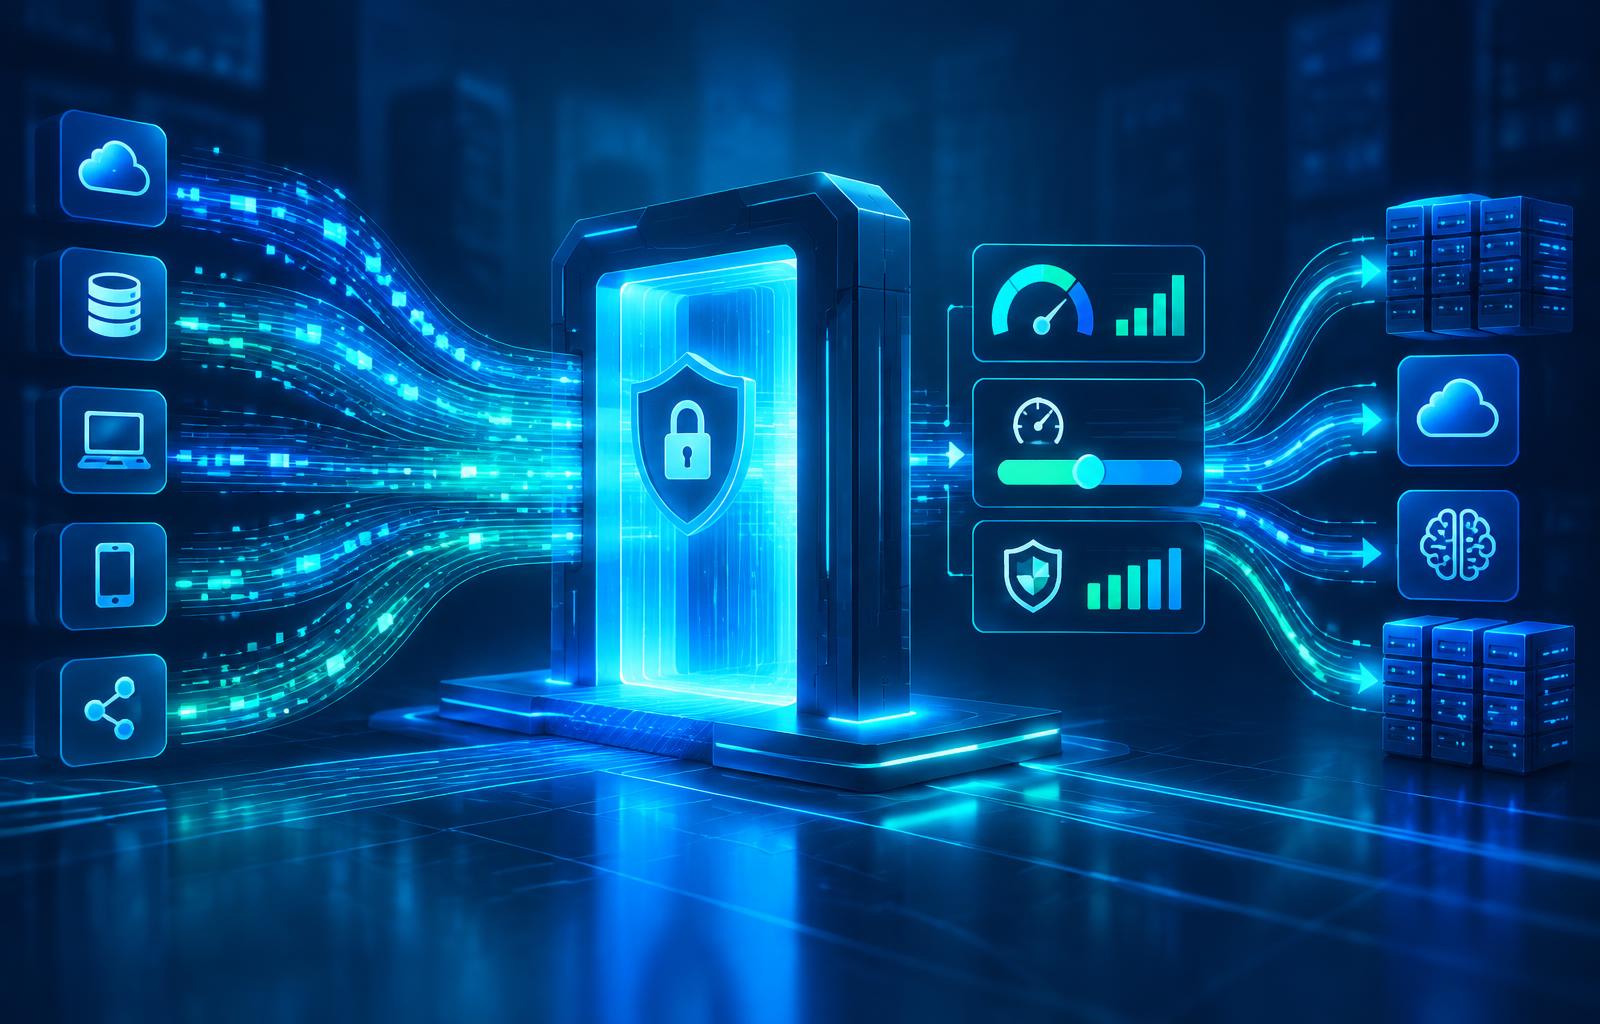
Illustration of AI requests passing through a central security gateway to model infrastructure

Enterprise AI infrastructure · Developed by CSP Solutions

BrainShift AI Gateway

One Gateway. Every AI Model. Total Enterprise Control.

Secure, govern, optimize, and scale enterprise AI through one intelligent gateway. Connect enterprise applications, AI agents, and employees to approved models in the cloud, private infrastructure, or on premises.

Control requests through enterprise policies, intelligent routing, load balancing, data protection, cost controls, and auditability—with CSP Solutions supporting architecture, integration, and deployment.

Security

Guardrails, identity & redaction

Intelligence

Routing & workload balancing

Efficiency

Budgets, quotas & cost visibility

Control

Monitoring, audit & governance

The enterprise control plane

Bring every model under one policy layer.

BrainShift

AI adoption creates a growing network of applications, providers, employee assistants, and autonomous workflows. BrainShift AI Gateway sits between that demand and the models that fulfill it, giving CIOs, CTOs, CISOs, architects, and AI teams a common point of control.

For government, financial services, and regulated enterprises, the objective is not simply access to more models. It is consistent policy enforcement, transparent operating costs, resilient routing, and clear accountability across the AI estate.

Explore the BrainShift product

Core capabilities

Twelve capabilities. One enterprise gateway.

01

Unified AI Model Access

One standardized API for enterprise applications and agents. Add or replace approved providers without rebuilding every integration.

Technical details

Connect supported OpenAI, Azure AI, Anthropic Claude, Google Gemini, DeepSeek, Meta Llama, AWS Bedrock, and private endpoints. Integration availability is confirmed for your deployment.

02

Intelligent Model Routing

Choose models by task, sensitivity, availability, latency, and cost—not just a fixed endpoint.

Technical details

Configure routing rules and approved model pools around request type, task complexity, model capabilities, and enterprise policies.

03

AI Load Balancing

Distribute traffic across available providers and endpoints to manage capacity and demand.

Technical details

Use provider health, capacity-aware routing, traffic allocations, and workload priorities to reduce reliance on one deployment.

04

Security Guardrails

Enforce input validation, content policies, and approved model access at the gateway.

Technical details

Configure prompt-injection controls, unsafe-content filtering, output policies, and application-specific rules. Guardrails reduce risk; they do not guarantee detection of every threat.

05

PII Detection & Redaction

Identify and mask protected information before requests reach external providers.

Technical details

Configure email, phone, identity, financial, document, and enterprise-defined patterns. Detection coverage and redaction behavior must be validated for the organization's data.

06

Enterprise Identity & SSO

Control access for people, applications, and services through a common policy layer.

Technical details

Scope identity-provider integration, SSO, roles, API keys, group permissions, and department-specific model access to the agreed architecture.

07

Rate Limits & Quotas

Manage requests, tokens, and concurrent workloads across teams and applications.

Technical details

Apply per-user, department, application, provider, and model policies. Limits help manage runaway consumption, protect capacity, and prioritize critical workloads.

08

Cost Optimization

Understand token consumption, allocate costs, and make cost-aware routing decisions.

Technical details

Compare model costs, define budgets and spending limits, review usage trends, and balance efficiency against the quality your workload requires.

09

Automatic Failover

Switch to approved alternatives when endpoints are unavailable or overloaded.

Technical details

Configure health checks, retries, fallback models, and traffic redistribution. Fallback rules must preserve data-handling and approved-destination restrictions.

10

Monitoring & Analytics

See request volumes, tokens, response times, errors, and provider performance together.

Technical details

Review latency percentiles, availability, estimated costs, consumption attribution, and routing or failover events through centralized operational reporting.

11

Audit & AI Governance

Trace model selection, access, policy events, and administrative activity.

Technical details

Configure audit retention and privacy policies. Operational metadata can be recorded without universally retaining sensitive prompt or response content.

12

Model Registry

Manage approved models, provider endpoints, model pools, and allowed uses centrally.

Technical details

Maintain a catalog of available models, capabilities, access rules, fallback configurations, and usage reports for public and privately deployed environments.

Enterprise AI architecture

A governed path from application to model.

BrainShift AI Gateway Core

Inspect sensitive data and enforce policies before routing. Approved destinations and fallback paths are constrained by your data-handling requirements.

Request lifecycle

Every AI Request. Governed From Start to Finish.

STEP 01

Authenticate

Validate the application, API key, identity, and model-access permissions.

Data security & governance

Inspect first. Route only to approved destinations.

A central enforcement layer makes it possible to apply consistent identity, content, and data policies before an application reaches an external provider. Redaction rules and model permissions can be adapted to organizational requirements.

Restrict sensitive workloads to approved private endpoints, and ensure fallback routes honor the same restrictions. Audit retention should reflect privacy requirements rather than automatically storing every sensitive prompt.

Illustrative redaction flow

Incoming request · fictional sample

Review the account for alex@example.com

Inspect → mask → validate policy

Approved outbound request

Review the account for [EMAIL_REDACTED]

Security controls, detection coverage, retention, infrastructure isolation, and data-location requirements are validated for the agreed deployment. No universal certification, residency guarantee, or perfect threat detection is implied.

Deployment options

Deploy Enterprise AI Under Your Control.

Choose an architecture aligned with your governance and operational requirements. Kubernetes and OpenShift deployment options are scoped with your infrastructure teams.

On Premises

Run the gateway in your own data center, with private model endpoints and enterprise operations scoped around your requirements.

Private Cloud

Operate in dedicated enterprise environments with agreed networking, access, and operational responsibilities.

Hybrid AI

Connect approved cloud LLMs and privately hosted models through common identity, routing, and data policies.

Sovereign AI Infrastructure

Define approved regional and processing boundaries. Sensitive traffic can be restricted to appropriately hosted models.

Restricted or disconnected deployments depend on configured model endpoints and supporting infrastructure. Provider and environment compatibility are confirmed before implementation.

Enterprise benefits

Stronger control. Less fragmentation.

Centralized AI Control

Manage model access and policies through a common control plane.

Stronger Data Protection

Apply consistent masking, access, and data-handling policies.

Cost Efficiency

Improve visibility, select suitable models, and manage consumption.

Improved Reliability

Reduce single-provider dependency with approved fallbacks.

AI Vendor Independence

Keep applications connected while changing approved providers.

Enterprise Scale & Governance

Attribute usage across departments, users, applications, and agents.

Operational visibility

See the AI estate. Understand every decision.

Gateway Operations

Illustrative dashboard · not customer results

Total requests

128,400

Active providers

4

Token consumption

18.6M

Estimated monthly spend

$2,840

Model usage distribution

Enterprise cloud45%
Private inference35%
Approved public APIs20%

Provider response latency

Enterprise cloud
640 ms
Private inference
480 ms
Approved public APIs
820 ms
Request success rate
99.2%

Enterprise use cases

One gateway across critical enterprise workflows.

Government & Sovereign AI

Control approved public and private model access, enforce data-handling boundaries, and maintain oversight of government AI services.

Banking & Financial Services

Unify authentication, consumption limits, policy enforcement, and auditable access for regulated workloads.

Enterprise AI Assistants

Provide governed LLM access to employee companions, knowledge assistants, and business applications.

AI Agents & Automation

Manage the routing, security, consumption, and operational costs of agents executing multi-step workflows.

BrainShift ecosystem

One Gateway Across the BrainShift Ecosystem.

BrainShift AI Workspace

Apply common model permissions and consumption policies to employee assistants and enterprise knowledge requests.

Explore Workspace

BrainShift Studio

Give agents, AI applications, and intelligent workflows access to models approved by the gateway.

Explore Studio

BrainShift AI Agents

Bring autonomous and assisted model requests under shared routing, cost, monitoring, and security controls.

Explore AI Agents

Gateway also serves third-party enterprise applications independently of other BrainShift products.

Enterprise engagement

Flexible Enterprise Deployment and Licensing.

Enterprise AI Gateway License

Centralized model access, policy management, and governance for multiple applications and departments.

Private or On-Premises Deployment

Enterprise-controlled deployment with architecture planning, integration, and agreed support options.

Enterprise Managed AI Gateway

Operations, provider configuration, traffic monitoring, and technical support under an agreed service contract.

Capabilities, provider integrations, deployment options, service levels, and commercial terms are confirmed against your requirements. Pricing is provided by quotation.

Frequently asked questions

The details enterprise teams need.

What is BrainShift AI Gateway?

A centralized infrastructure and governance layer between enterprise applications and AI models. It brings access policies, routing, usage controls, and operational visibility into one platform.

Can we connect multiple LLM providers?

Yes. Supported internal and external endpoints can sit behind one standardized API. CSP Solutions confirms the required providers, credentials, licensing, and integrations for your deployment.

Can we connect privately hosted models?

Yes. Compatible private inference services can join approved model pools alongside cloud models, with rules governing which workloads may use each destination.

Does it support on-premises deployment?

On-premises and private-cloud architectures are available for scoping. Restricted or disconnected operation depends on local model endpoints and all supporting infrastructure.

How does it protect sensitive enterprise data?

Configurable redaction, PII detection, guardrails, access policies, and destination restrictions help control data handling. Controls must be tested for your data and are not a blanket compliance guarantee.

How does intelligent routing work?

Policies select from approved models using factors such as task type, sensitivity, cost, latency, capacity, and availability. Your teams define the permitted choices.

What happens when a provider is unavailable?

Configured health checks, retries, and fallback policies can redirect requests to approved alternatives. A fallback must not bypass your security or data-location restrictions.

Can we control spending by department?

Department and application attribution, quotas, budgets, and spending controls support cost oversight. Metering and budget behavior are agreed for the deployment.

Does it support enterprise SSO?

Enterprise identity and SSO integration can align gateway access with your directory. Identity-provider compatibility and permission mapping are confirmed during implementation.

Do existing applications need major changes?

Applications can generally connect to the gateway instead of directly to models. Compatibility, authentication, request formats, and any application changes are assessed during integration.

Can it run on Kubernetes or OpenShift?

Container orchestration options can be scoped for Kubernetes and OpenShift. Cluster versions, networking, storage, observability, and support responsibilities are confirmed in the architecture review.

How does it integrate with Workspace and Studio?

Workspace employee requests and Studio agent workflows use the gateway's approved models and policies. Third-party enterprise applications can also use Gateway independently.

Talk to CSP Solutions

Take Control of Your Enterprise AI Infrastructure.

Unify AI model access, protect enterprise information, optimize performance, and govern consumption. Discuss cloud, private, and on-premises deployment with CSP Solutions.

Privacy policy
sales@cspsolutions.com